
Why a Smart-Card Wallet Makes Sense: Protecting Private Keys with NFC and Multi-Currency Support
Why Liquidity Mining, Gas Optimization, and dApp Integration Are Game-Changers in Web3 Wallets
februarie 5, 2025Why I Stopped Trusting Cloud Backups for My Seed Phrase (and What I Use Instead)
februarie 19, 2025Okay, so check this out—I’ve been messing with crypto gear for years, and smart-card wallets keep pulling me back. Whoa! They feel like a tiny, stubborn piece of hardware that refuses to be hacked, in the way a good old New York lock does. My instinct said smart-cards would be gimmicky at first, but they actually solve a few hard problems pretty elegantly. Initially I thought they’d be clunky, but then I realized that the card form factor is underrated for daily usability and security combined.
Seriously? I mean, really—holding your private key on something that fits in your wallet changes your behavior. Hmm… There’s comfort in a tactile object you can see and touch. On one hand, people worry about losing a card; on the other hand, people lose phones all the time and those are far more vulnerable to online attacks. Actually, wait—let me rephrase that: the risk profile shifts, not disappears; it becomes about physical custody instead of remote compromise.
Here’s the thing. Shortcuts like screenshots or copying keys into cloud notes feel convenient, but they create single points of failure. Wow! You don’t need a lecture on „hot vs cold” wallets; you know the terms. But you might not know how an NFC-capable smart card actually isolates secrets. So I want to walk through that, from the user perspective, without being too nerdy.
Smart-card wallets keep the seed or private key inside a secure element that never reveals it. Seriously? Yes—the device signs transactions internally and only outputs signatures, not the key itself. That design is crucial because it prevents malware on your phone or desktop from trivially exfiltrating keys. On top of that, the card’s NFC lets you sign things without plugging in cables, which is convenient enough to encourage safer behavior.
Something felt off about early NFC attempts, though. Whoa! They were slow or flaky sometimes, especially with older phones and weird cases. But modern implementations are much better, and when the firmware is solid, NFC really shines for user experience. I’m biased, but I prefer tapping a card to fumbling with cables at a coffee shop.
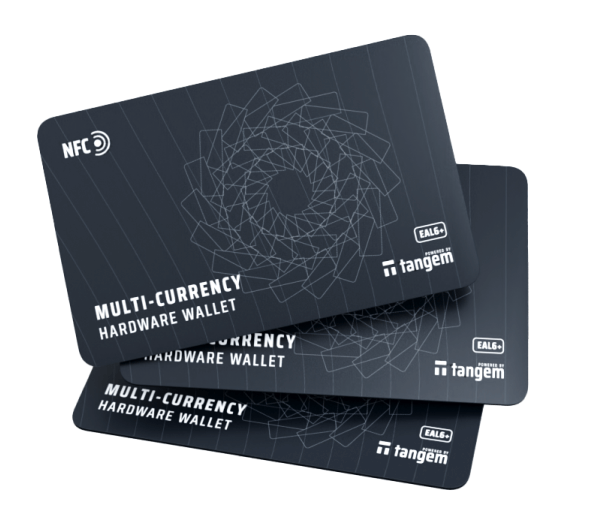
A practical view: private key protection and user habits
Think of the secure element like a bank vault with a tiny keypad. Hmm… You don’t get to see the money inside; you get confirmation that a transaction went through. That mental model helps people accept a black-box system. Initially I worried users would distrust something they can’t inspect, though actually most accept bank cards and ATMs without issue. On balance, this approach reduces attack surface dramatically compared to storing keys on an internet-connected device.
My experience in Silicon Valley startups taught me that convenience wins. Whoa! If security is arduous, users find workarounds. So the sweet spot is strong protection with low friction. A smart-card with NFC does that—tap, review, confirm. It feels familiar, like using a contactless credit card, and that familiarity nudges people toward safer behavior. Also, the tactile habit—slipping a card into your wallet—reinforces custody.
There are caveats. Hmm… Backups matter. If you rely solely on one physical card and it gets lost, you’re in trouble. On the other hand, you can provision multiple cards as backups or use passphrase-protected seeds to split risk. I’m not 100% sure everyone will bother to set up multiple backups, but the option exists. And yes, multisig setups can further distribute trust across devices and people.
Also, smart-card wallets excel at isolating the private key from hostile environments. Whoa! When a transaction is built on your phone, only the unsigned transaction travels to the card; the card signs it and sends back the signature. That separation means even a fully compromised phone can’t steal the seed. That pattern—build off-device, sign on-device—feels simple but it’s powerful, and it’s what differentiates real hardware-based security from „software wallets with encryption.”
Now about multi-currency support. Wow! Not all cards are created equal. Some are single-chain focused, while others are broad and adaptable. My first card only supported Bitcoin and a handful of tokens and that was annoying. But modern smart-card wallets often support multiple keys and can work with companion apps that translate signatures for different chains. Initially I thought this would be messy to implement, but the right card firmware plus good app integration makes it pretty smooth.
Here’s a concrete example. Imagine you hold BTC, ETH, and a couple of tokens on Solana. You tap your card, the app constructs the appropriate transaction format for the chain, the card signs it using the right key schema, and the signature returns—done. On one hand, users want one wallet to rule them all. On the other hand, blockchain diversity means more complexity under the hood, and the user experience must hide that complexity without breaking security guarantees.
I’ll be honest—this part bugs me when companies oversell „universal” support. Wow! Universal is a slippery word. In practice, adding support for a new chain sometimes requires firmware updates, new derivation paths, and careful testing to avoid edge cases. (oh, and by the way…) That maintenance is real work, and it’s where a lot of vendors cut corners.
Why NFC though? Good question. Short answer: it combines usability with security. Seriously? Yep. NFC avoids exposing USB interfaces that could be abused and keeps interactions local. NFC has limited range and the communication can be constrained to a single session, which reduces attack vectors. But it’s not a panacea; NFC pairing must be implemented correctly and physical proximity doesn’t equal absolute safety.
In practice, NFC simplifies mobile-first workflows. Whoa! You can sign on the go. But you still need to verify transaction details on a secure screen or the card’s tiny display if it has one. My instinct said that users would ignore big details, and sadly that sometimes happens—people tap without checking amounts. Design must encourage verification, for example by showing key recipient info prominently and requiring conscious gestures to confirm.
Let’s talk about a real workflow I tested. Really? Yes—I used a smart-card wallet to move funds across chains during a hectic airport layover. Whoa! The card made it quick; tapping, approving, and walking away. Later, in a calmer setting, I duplicated the setup for backup cards at home. That experience reinforced the notion that simplicity in secure key handling increases the chance people actually do the right thing. There’s a human tendency to choose convenience repeatedly, and security design should work with that tendency, not against it.
Security-wise, the threat model shifts when you move to a smart-card. Hmm… Attackers now focus on the supply chain, firmware exploits, and physical coercion. Initially I underestimated supply chain risk; then I saw reports about tampered devices and it changed my view. On one hand, buying from a trusted vendor reduces that risk considerably. On the other hand, you should still verify device provenance and updates—like you would with any high-stakes tool.
One feature I prefer is the ability to pair a card with multiple interfaces while keeping the key locked. Whoa! That allows desktop cold-signing via an NFC reader and mobile signing via smartphone. It’s versatile. I’m biased toward workflow flexibility because my life and devices are messy—phones die, laptops fail, the subway swallows unknown things—so I like redundancy. Still, every added interface is another potential misconfiguration point, so simplicity is a virtue.
Okay, a few practical tips for anyone considering a smart-card. Whoa! First, buy from reputable sources and verify tamper evidence. Second, provision at least one backup card or a secure seed with passphrase protection. Third, test recovery in a safe environment so you’re not surprised later. Fourth, keep firmware updated—but only after verifying update signatures and reading changelogs. These steps sound obvious, but people skip them, and that’s how losses happen.
Frequently asked questions
Can a smart-card really replace traditional hardware wallets?
Short answer: it depends on your needs. Smart-cards offer excellent portability and low friction, and they often match hardware wallets on key isolation. However, if you need large displays, complex multisig, or advanced scripting, some full-featured hardware devices may still be preferable. For everyday users who want strong protection and NFC convenience, smart-cards hit the sweet spot.
How does multi-currency support actually work?
The card stores multiple keypairs or a master seed derivation schema, and companion apps translate chain-specific transactions into formats the card can sign. It’s seamless when implemented well, but adding new chains can require firmware or app updates. I’m not saying it’s trivial—it’s just manageable when vendors invest in good integration.
Where can I learn more or try one?
Check out the tangem hardware wallet for an example of a smart-card approach that blends NFC usability with secure elements and multi-currency capabilities. I’m mentioning it because I’ve handled similar devices and found the form factor compelling for daily crypto custody.


